
Wordfence Security
Endpoint firewall, malware scanner and login security plugin for WordPress, with paid tiers for real-time threat data and hands-on incident response.
80

Vulnerability intelligence and virtual patching for WordPress: free alerts for up to 3 sites, paid firewall rules that block exploits before you update.

Patchstack approaches WordPress security from the vulnerability side. It runs one of the largest vulnerability disclosure programmes for WordPress plugins and themes, and the plugin matches the software installed on your site against that database. Rather than scanning for malware after an infection, the aim is to stop known flaws from being exploited in the first place.
The free plan is detection only. It lists vulnerable plugins, themes and core versions, sends email alerts (with intelligence that can arrive up to 48 hours before public disclosure), offers optional automatic updates for vulnerable plugins only, produces snapshot PDF reports and lets you monitor up to three sites from the Patchstack app. It adds no firewall and runs only scheduled tasks, so it has almost no performance impact.
Paid protection, from $5 per site per month or the Developer plan for 25 sites, turns on virtual patching: targeted mitigation rules (Patchstack quotes 12,000+) that block exploit attempts against specific vulnerable components without changing their code. Paid sites also get custom firewall rules, a community IP blocklist, two-factor authentication, login page protection with reCAPTCHA, and a hardening module that disables the theme editor, blocks user enumeration, restricts XML-RPC and the REST API to logged-in users, hides the WordPress version and adds a standard set of security headers through .htaccess. Higher plans add API access, scheduled reports, SLAs and compliance paperwork.
Patchstack is deliberately not an all-in-one suite. It has no malware scanner, no file integrity checks and no cleanup service, and its login protection replaces the usual hidden-login trick with a secret-link allowlist. Many people run it alongside another security or backup plugin. Its virtual patching is also offered by several hosts and management tools that resell Patchstack.
It is the best fit for agencies and developers who manage many sites and want early vulnerability warnings and exploit blocking without waiting for every vendor to ship a fix.
Best for: Agencies and developers who want early vulnerability alerts and virtual patching across many WordPress sites.
Patchstack is the specialist pick for stopping plugin vulnerability exploits, and its free alerts are useful on any site. It is not a full security suite, so plan to pair it with a malware scanner or backup tool; the paid plans are worth it mainly when you manage enough sites to justify them.
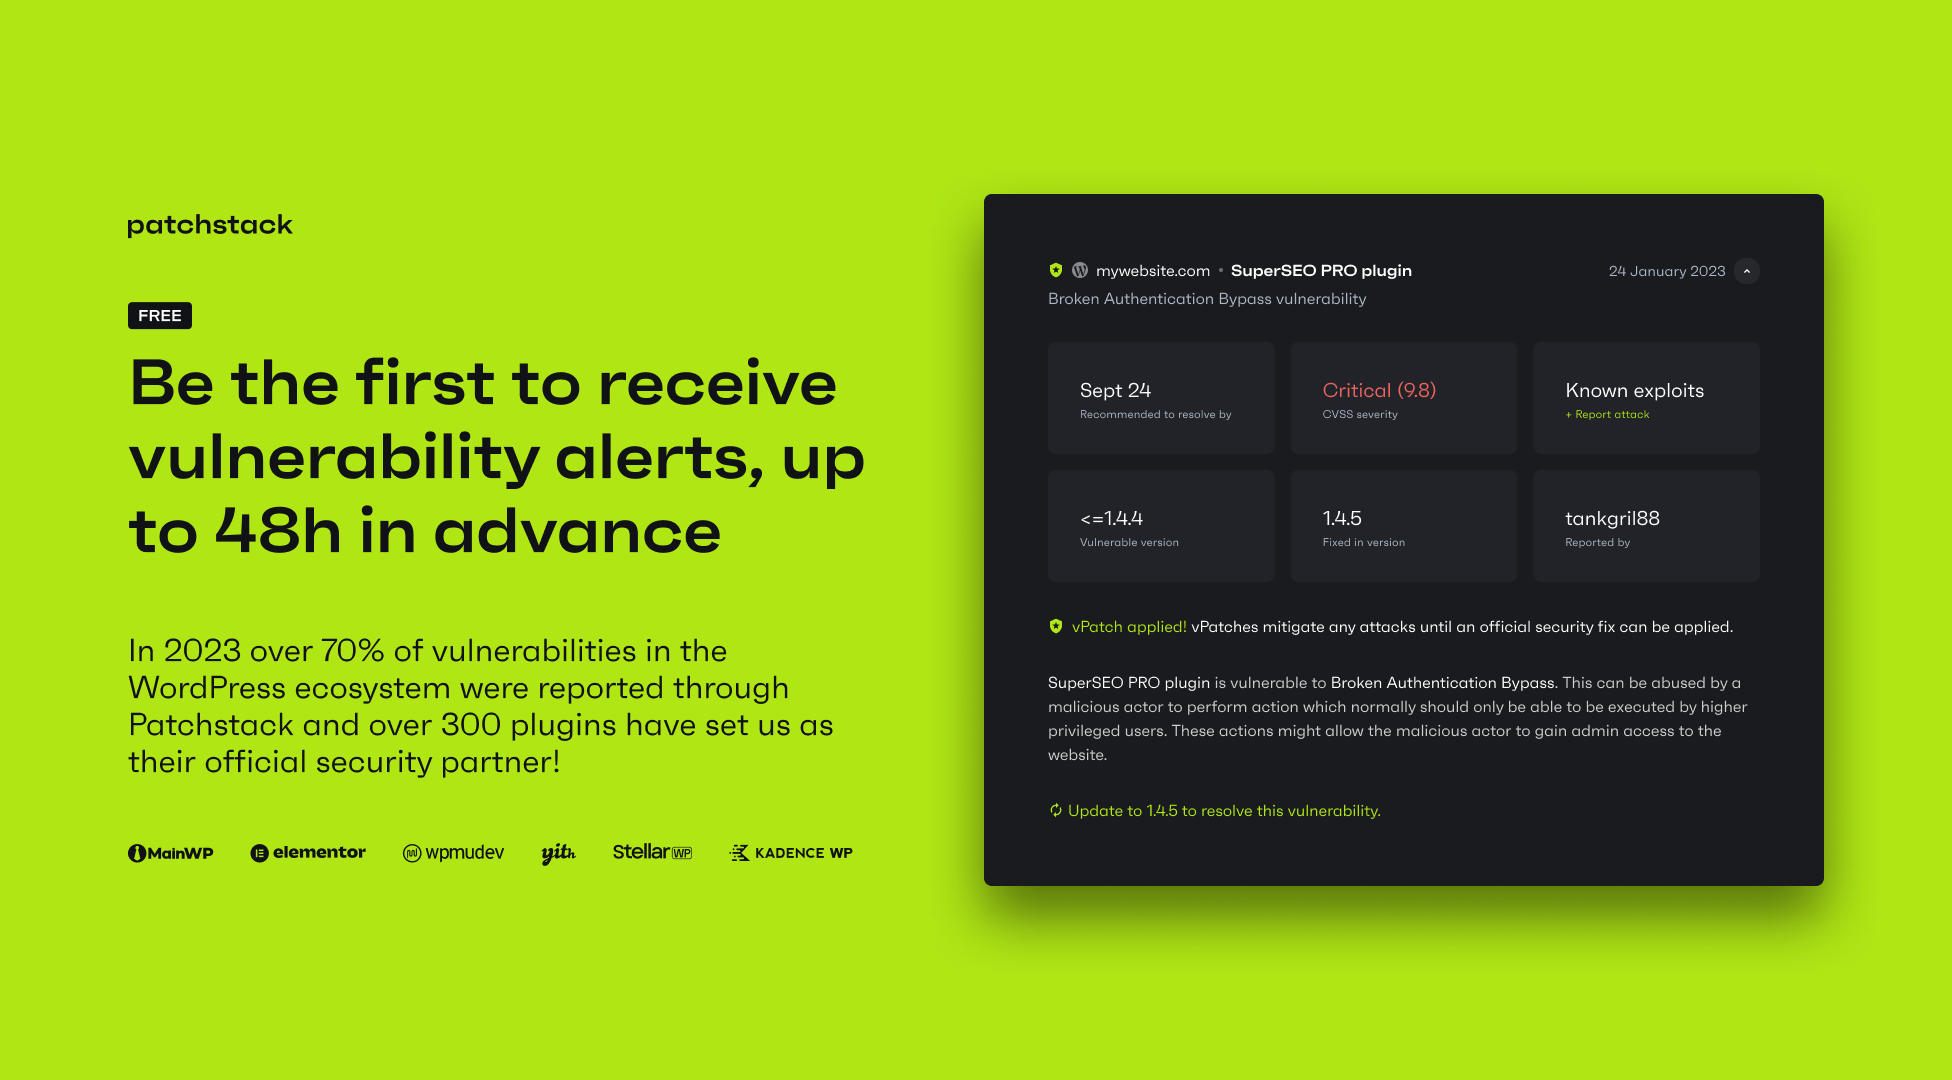
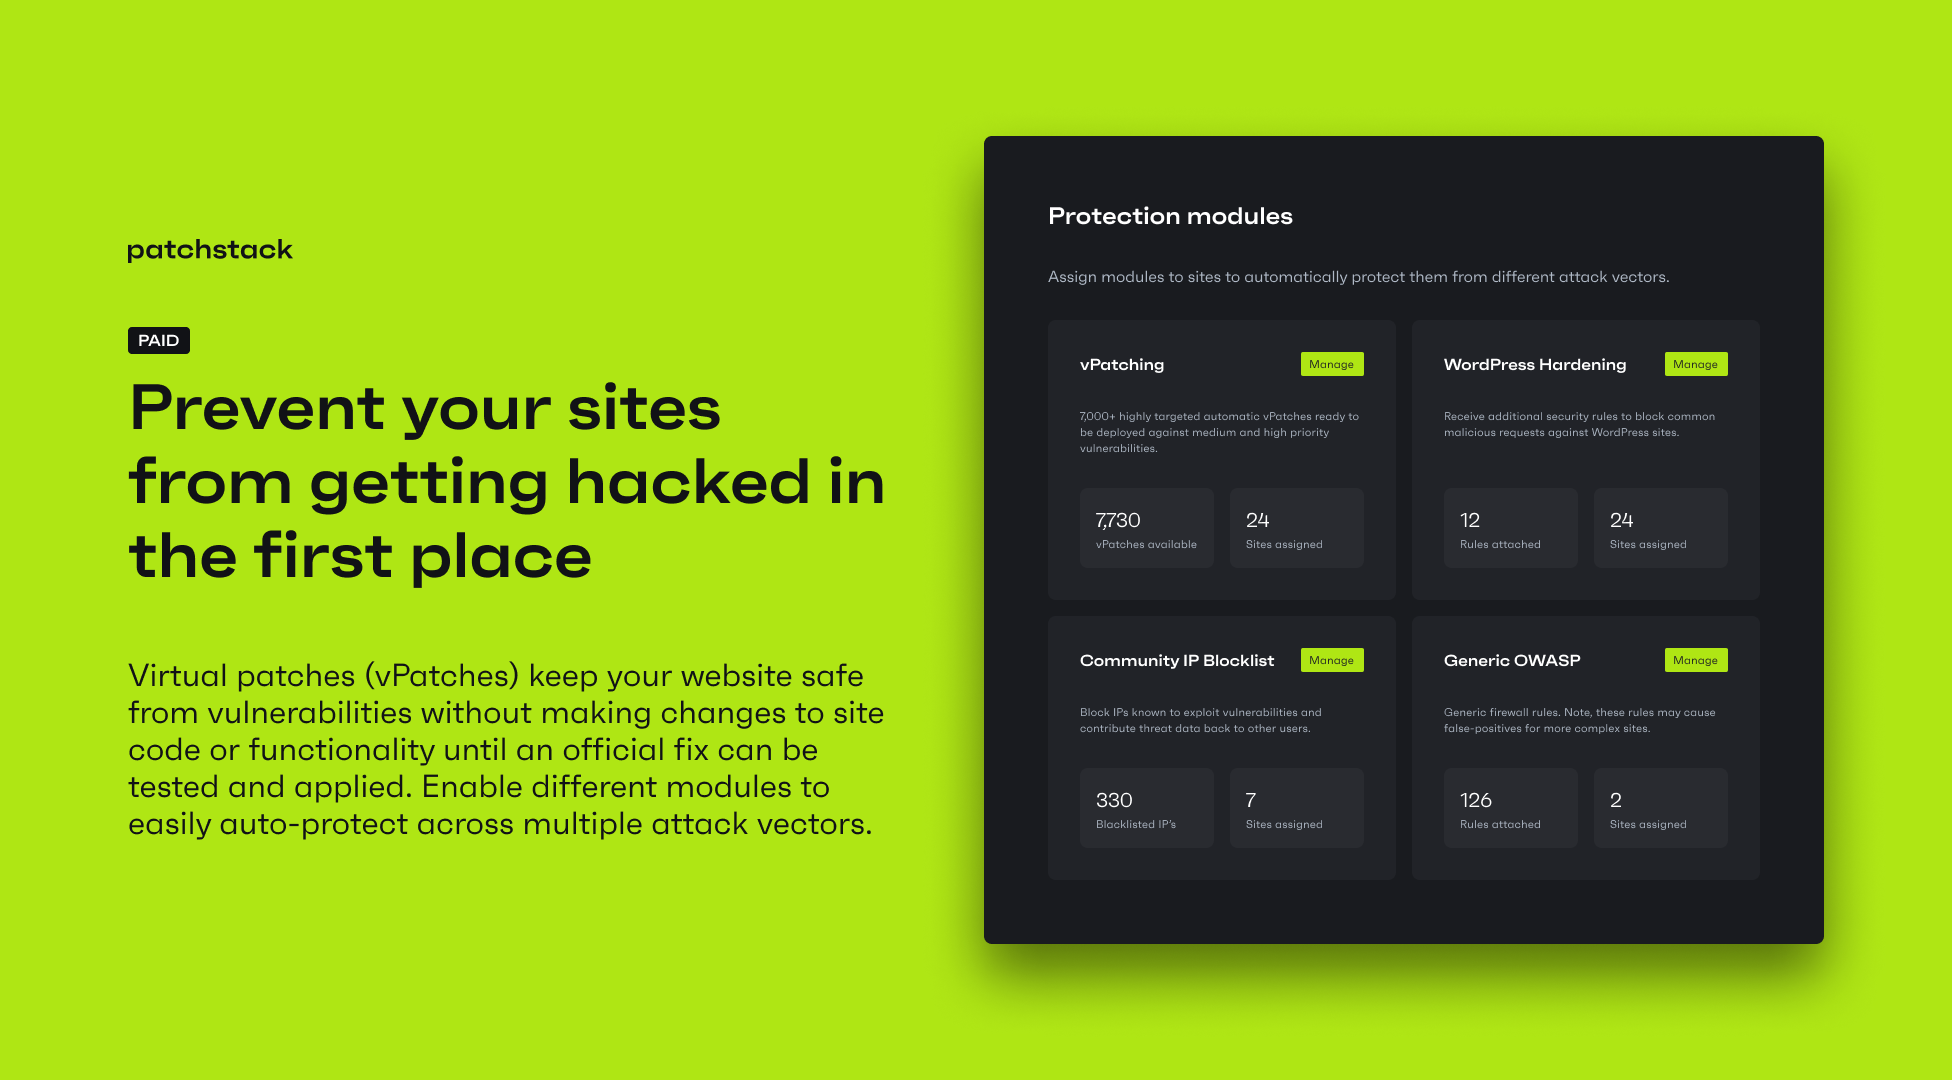
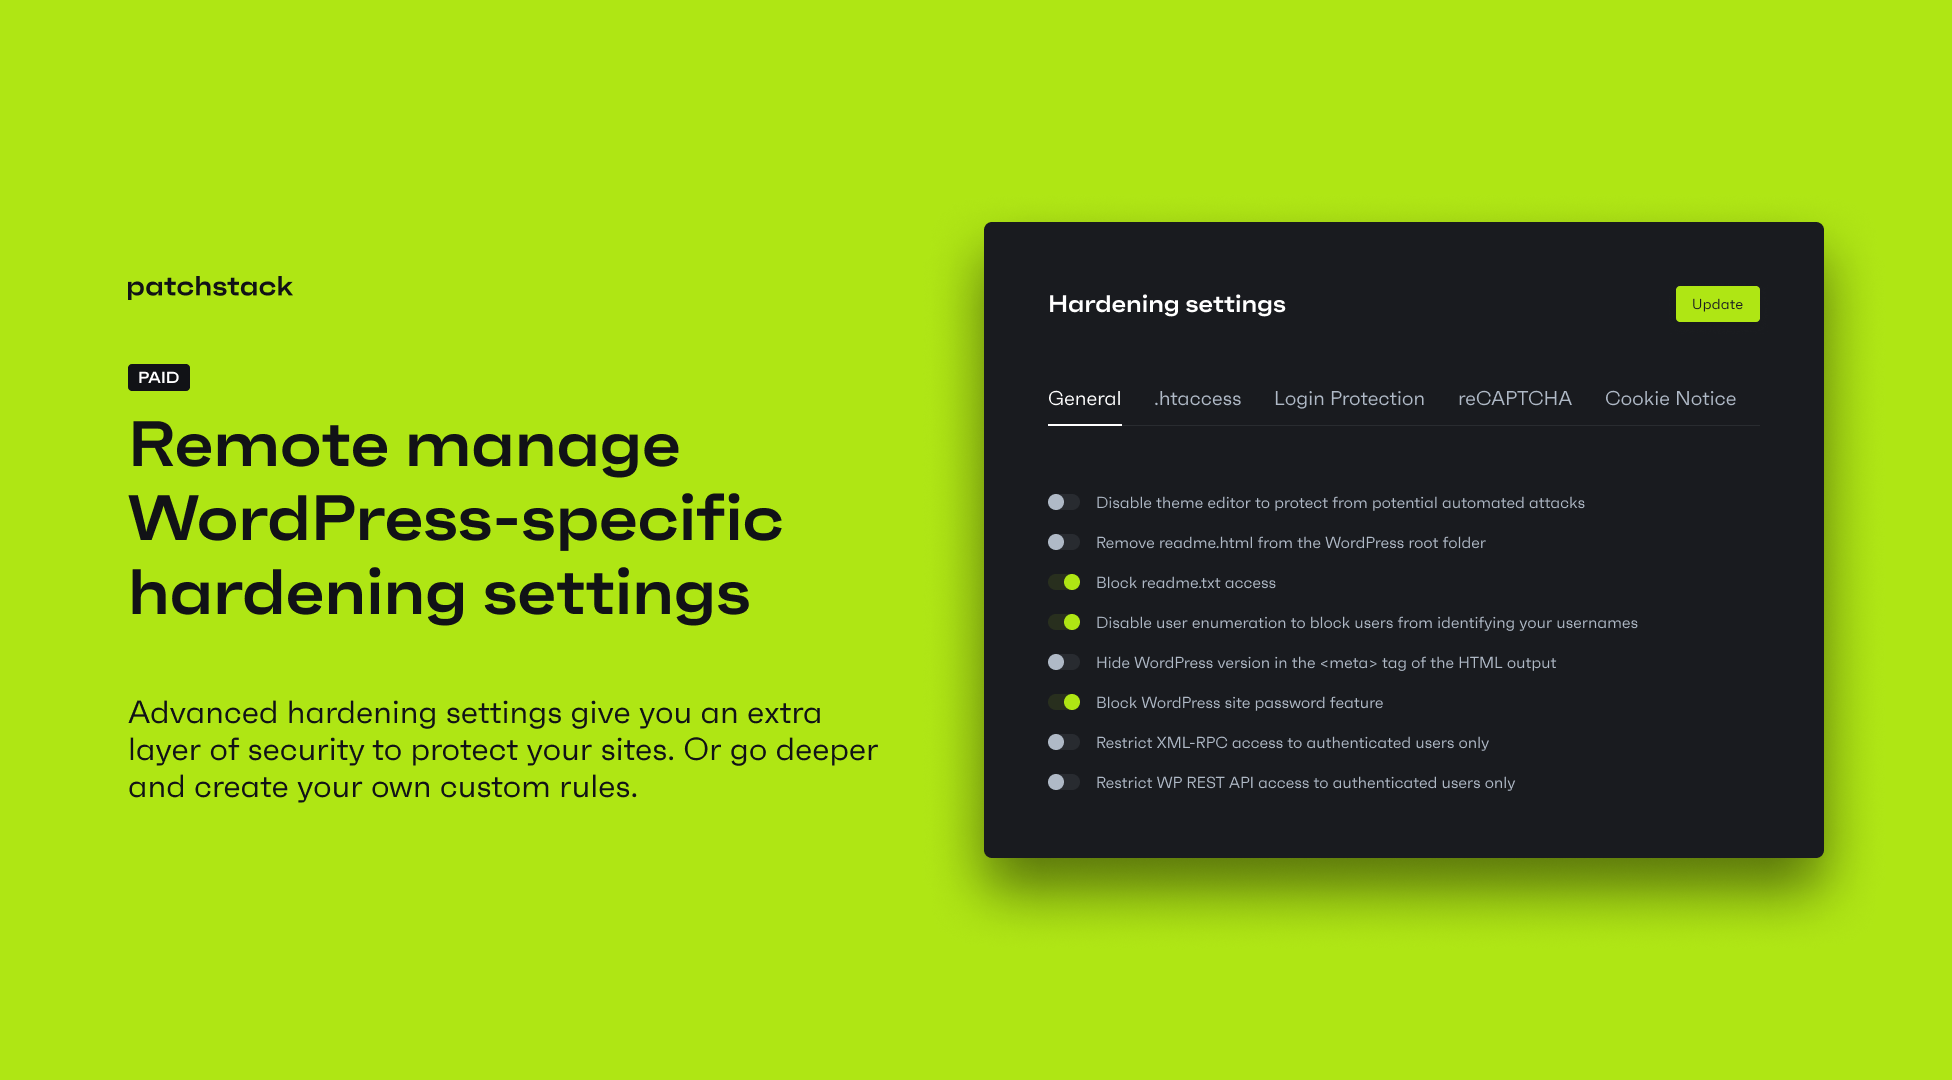
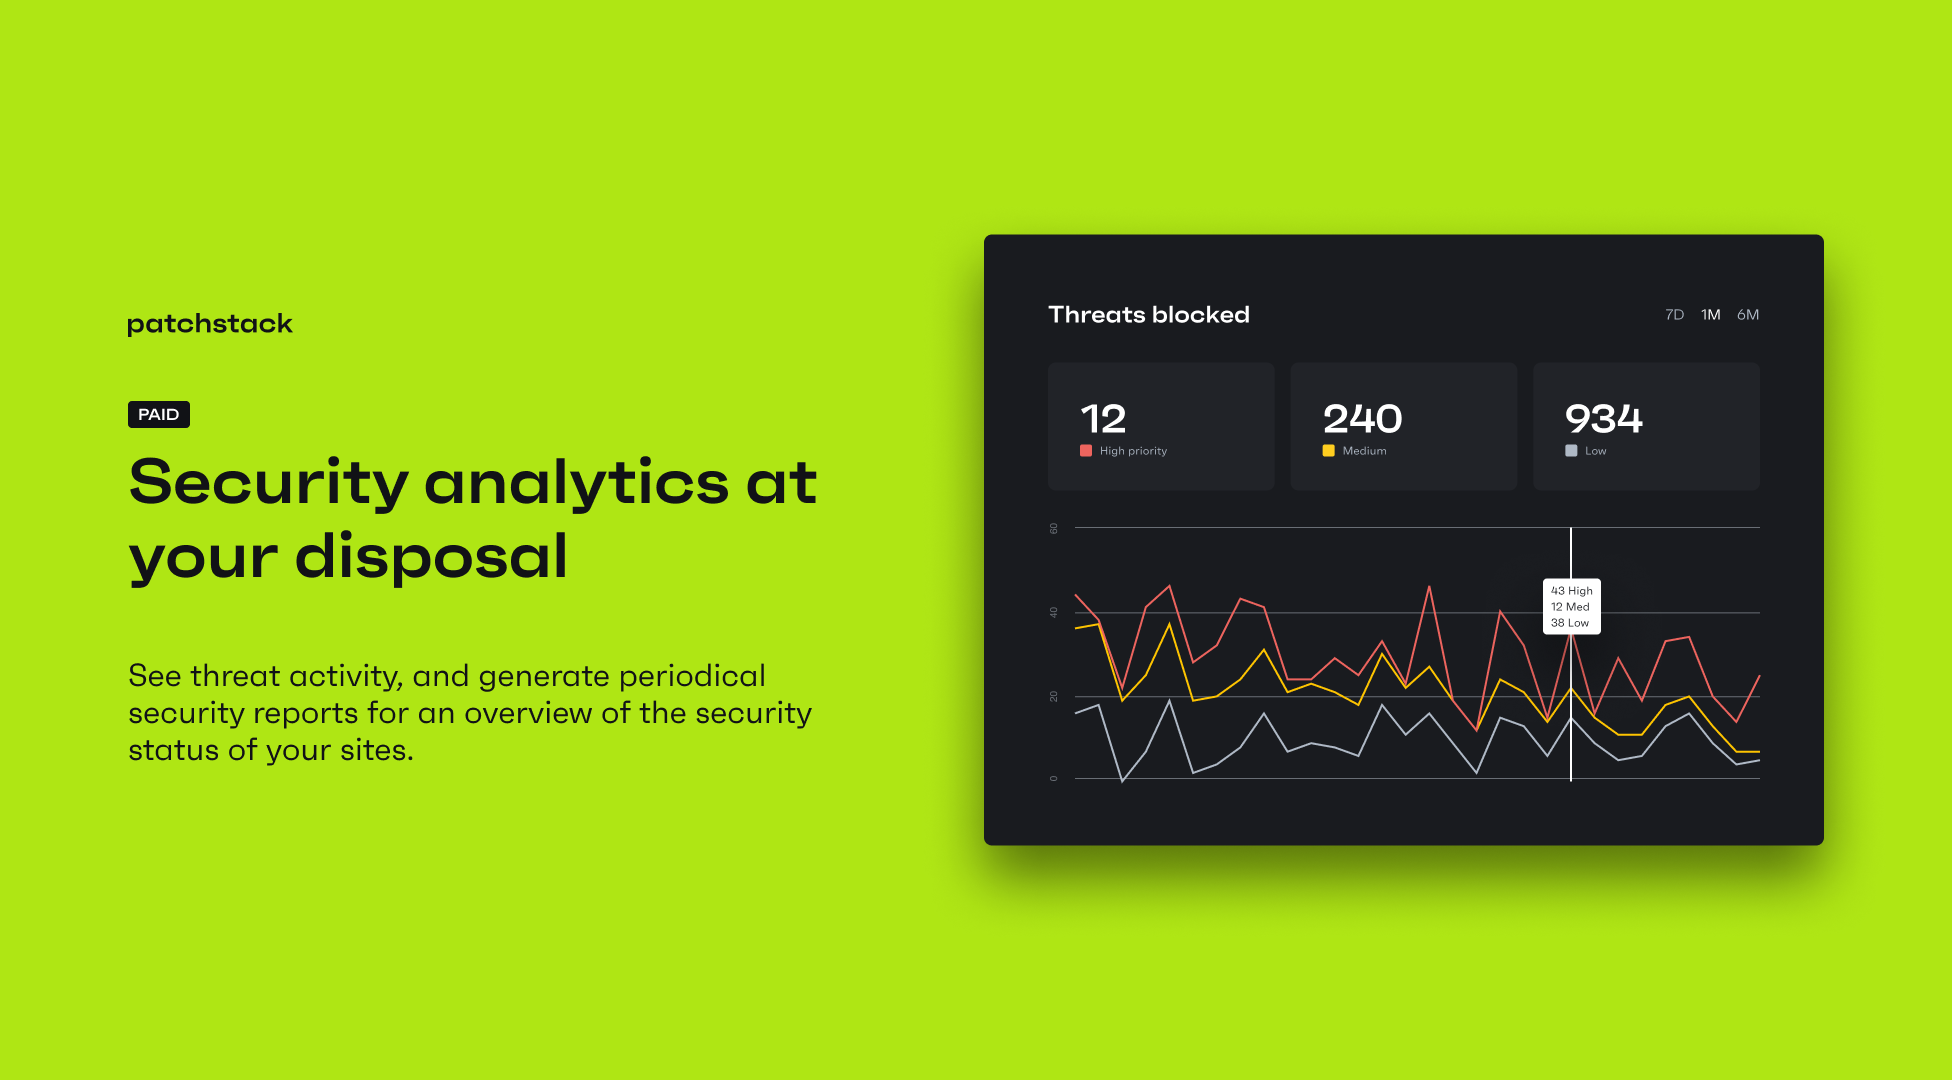
What Patchstack highlights on its WordPress.org page and its own website, split by version.
16 of 26 features we track in Security Plugins, feature score 60/100
Filters malicious requests (SQL injection, XSS and similar) before they reach WordPress.
Paid plans filter requests with vPatch rules and unlimited custom firewall rules; free has no firewall.
Firewall runs on the vendor's network in front of your server, not inside WordPress.
Rules are enforced by the plugin on each page load, not on a vendor proxy.
Limits failed logins and locks out attackers guessing passwords.
Paid login protection blocks wp-login.php except via a secret allowlisting link; rate limiting in hardening.
CAPTCHA or Turnstile on login, registration and password reset forms.
reCAPTCHA is part of the paid remote hardening settings.
Throttles or blocks aggressive crawlers and bad bots.
Block or allow traffic by country.
Blocks IPs known for attacks using shared threat intelligence.
Community IP blocklist of known attacker addresses on paid plans.
Scans files and database for malware, backdoors and injected code.
Vendor states the product focuses on prevention rather than malware scanning.
Compares core, plugin and theme files with originals and flags changes.
No file comparison or integrity checking is offered.
Warns when installed plugins, themes or core have known vulnerabilities.
Free detection of vulnerable plugins, themes and core using Patchstack's database.
Runs scans automatically on a schedule.
Software versions are checked automatically by scheduled tasks; there are no malware scans.
Scans run on the vendor's servers so they don't slow your site.
Vulnerability matching happens against Patchstack's cloud database; no offsite malware scanning.
One-click or expert cleanup of infected sites.
No cleanup service; Patchstack positions itself as prevention.
Second login factor via authenticator app, email or similar.
Two-factor authentication is included with paid protection.
Passwordless login with passkeys or hardware security keys.
Enforce strong passwords, expiry or breached-password checks.
Move or hide the wp-login.php / wp-admin login page.
Paid option blocks wp-login.php entirely and opens it via a secret link instead of renaming it.
View and end active user sessions, limit concurrent logins.
Disable XML-RPC, file editing, user enumeration and similar weak points.
Disable theme editor, block user enumeration, restrict XML-RPC/REST API, hide WP version.
Enforce HTTPS, fix mixed content and redirects.
Set HSTS, CSP, X-Frame-Options and other HTTP security headers.
Hardening toggle adds a standard set of security headers via .htaccess.
Firewall rules that block exploits for known plugin vulnerabilities before an update is available.
Core paid feature: 12,000+ targeted mitigation rules blocking known exploits.
Automatically updates plugins with known vulnerabilities.
Free option to auto-update only plugins with known vulnerabilities.
Records logins, changes and admin actions for auditing.
Logs and analytics are included in the free plan as well.
Email or app alerts for attacks, lockouts and scan results.
Real-time email alerts for new vulnerabilities; Slack and custom alerts on paid plans.
Manage security for many sites from one dashboard.
Patchstack app shows security status for up to 3 sites free, more on paid plans.
On WordPress.org
1 site
Adds virtual patching to a site on the free Personal plan (free plan monitors up to 3 sites).
25 sites
$69/month billed yearly or $79 monthly; first month free; +5 sites for $12.50/month; 3 team seats. Enterprise and Web Host plans are custom-quoted.
Prices are list prices from the vendor's site, checked 14 Oct 2026. Many vendors discount the first year.
Free installs from WordPress.org, the vendor's own claim, and our estimate of paid installs.
Active installations reported by WordPress.org.
The vendor does not publish a total.
Our estimate, see method below.
How we estimated this: About 150K free installs x 12% (the usual share of free sites that also run the paid version when a hosted service whose free tier is limited) gives 18K. Likely range: 9K to 36K. This counts sites running the paid version, including sites whose licence has lapsed. Estimates are rough and based on public figures as of 14 Oct 2026.
6,615 downloads last week, 746.2K all time
| Version | 2.3.7 |
|---|---|
| Last updated | 28 Jul 2026 (97 days ago) |
| Tested up to | WordPress 7.0.8 |
| Requires | WordPress 5.2+, PHP 5.6+ |
| Support threads (2 months) | 0 of 1 resolved |
| On WordPress.org since | 1 Nov 2021 |
| Refund policy | 30-day money-back (source, 5 Oct 2026) |
|---|---|
| G2 rating | 4.9 (source, 5 Oct 2026) Rating shown on the Patchstack homepage. |
 All-In-One Security (AIOS)/Patchstack
 Patchstack/Really Simple Security
 Jetpack Protect/Patchstack
 Patchstack/WP Cerber Security
 Limit Login Attempts Reloaded/Patchstack
 MalCare Security/Patchstack
 Patchstack/Shield Security
 Defender Security/PatchstackPatchstack/Wordfence Security
 Patchstack/Kadence Security (formerly Solid Security)
 Patchstack/Sucuri Security
Endpoint firewall, malware scanner and login security plugin for WordPress, with paid tiers for real-time threat data and hands-on incident response.
Free auditing, file integrity and remote scanning plugin from Sucuri that connects to its paid cloud firewall and malware cleanup platform.
WPMU DEV's WordPress security plugin with malware scanning, AntiBot firewall, 2FA with passkeys, hardening and audit logs; Pro adds scheduled scans.
Automated WordPress security plugin with firewall, silentCAPTCHA bot detection, 2FA and audit log; ShieldPRO adds malware and vulnerability scanning.
Cloud-scanning WordPress security plugin with a plugin-level firewall, login protection and paid one-click malware cleanup, for site owners and agencies.
Login-focused WordPress security plugin (formerly Solid Security / iThemes Security) with 2FA, brute-force protection and Patchstack virtual patching in Pro.
Yes. Patchstack has a free version on WordPress.org. Paid plans start at $5/mo.
WordPress.org reports 100K+ active installations of the free version. We estimate around 18K sites run the paid version.
Yes: paid version (Personal protection). Paid plans filter requests with vPatch rules and unlimited custom firewall rules; free has no firewall.
Yes: paid version (Personal protection). Paid login protection blocks wp-login.php except via a secret allowlisting link; rate limiting in hardening.
No: not included. Vendor states the product focuses on prevention rather than malware scanning.
Yes: included. Free detection of vulnerable plugins, themes and core using Patchstack's database.
Yes: paid version (Personal protection). Two-factor authentication is included with paid protection.
Yes: included. Logs and analytics are included in the free plan as well.
No. Patchstack focuses on preventing infections by detecting and virtually patching known vulnerabilities. Use a separate scanner or cleanup service for malware.
Targeted firewall rules that block exploit attempts against a specific vulnerable plugin or theme without editing its code, so you are protected before an official fix is installed.
Yes for awareness: it alerts you to vulnerable software on up to three sites and can auto-update only the vulnerable plugins, but it does not block attacks.
Yes, but each subsite has to be added to your Patchstack account and uses one site slot.
Last updated 5 Oct 2026. Spotted something wrong? Suggest an edit.