
Sucuri Security
Free auditing, file integrity and remote scanning plugin from Sucuri that connects to its paid cloud firewall and malware cleanup platform.
87

Endpoint firewall, malware scanner and login security plugin for WordPress, with paid tiers for real-time threat data and hands-on incident response.
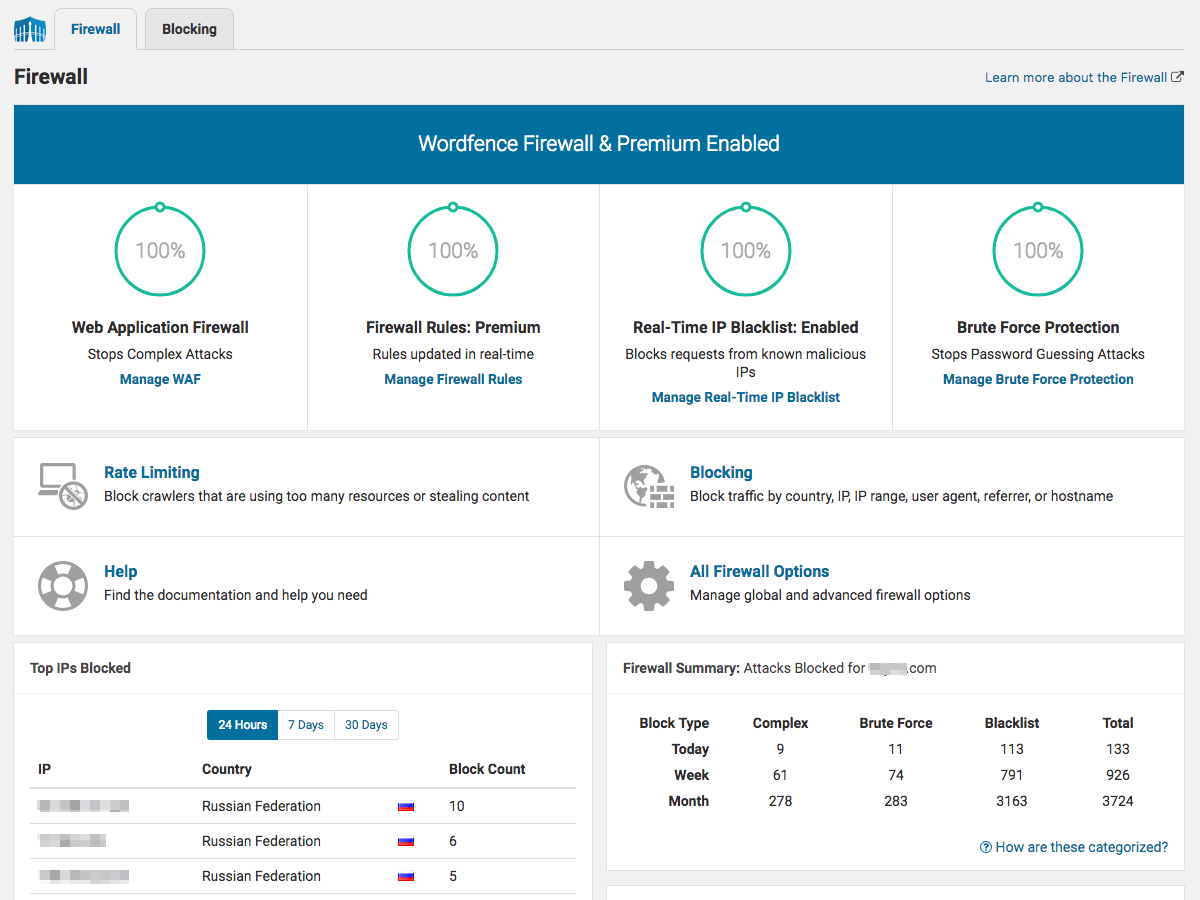
Wordfence Security is a security plugin from Defiant Inc. that runs entirely on your own server. Instead of routing traffic through a proxy, it installs an endpoint web application firewall that inspects requests inside WordPress, alongside a file and database scanner and a separate login-security module. The free plugin on WordPress.org already includes the firewall, the scanner, two-factor authentication and passkeys, which is why it is one of the most widely installed security plugins in the directory.
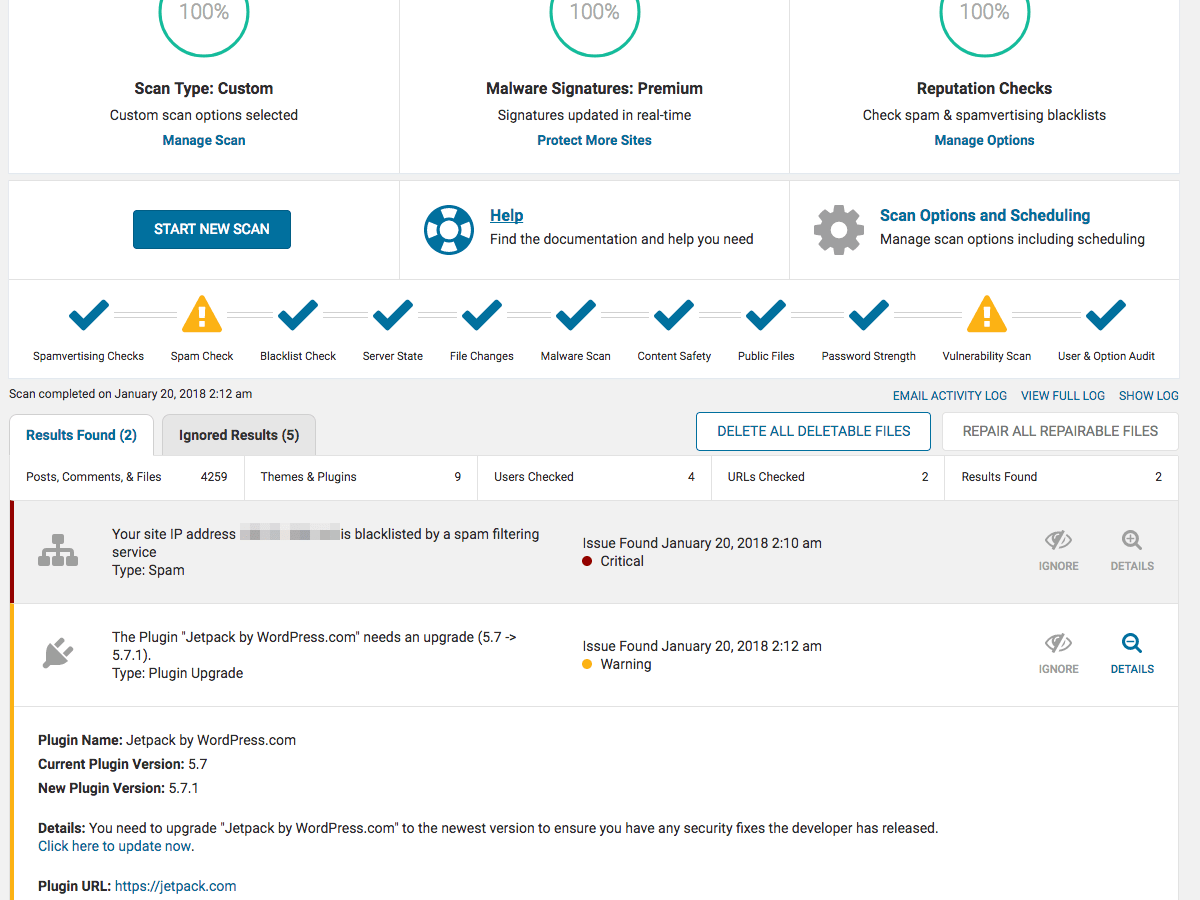
The firewall and scanner are fed by Wordfence’s Threat Defense Feed. Free sites receive new firewall rules and malware signatures 30 days after paying customers, while Premium sites get them in real time together with a real-time IP blocklist. The scanner compares core, theme and plugin files with the WordPress.org originals, looks for backdoors, injected code and malicious URLs, and flags plugins with known vulnerabilities or that have been abandoned. Live Traffic shows visits and blocked attacks as they happen.
Premium adds real-time rules and signatures, the IP blocklist, country blocking, more frequent scans, the Audit Log and ticket support. Care adds a dedicated analyst, a yearly security audit and hands-on malware cleanup, and Response adds 24/7 incident response with a one-hour response target. Each licence covers one site.
Because everything runs on your server, scans and firewall processing use your hosting resources, which can be noticeable on cheap shared hosting. There is no option to rename the login page, no HTTP security-header manager, no SSL tooling and no automatic updating of vulnerable plugins. The 30-day delay on free rules is a real gap for newly disclosed vulnerabilities.
Wordfence suits site owners who want a capable free firewall and scanner without a cloud proxy, and agencies who can use the free Central dashboard. Sites that need a CDN-based firewall, DDoS mitigation or lightweight scanning should look at a cloud option instead.
Best for: Site owners and agencies who want a strong free on-server firewall and scanner, with the option to buy real-time threat data or incident response.
Wordfence gives more real protection for free than most rivals: a genuine WAF, a thorough scanner, 2FA and passkeys. The 30-day rule delay and per-site pricing are the trade-offs, and it can feel heavy on weak hosting, but for most WordPress sites it is a sensible default.


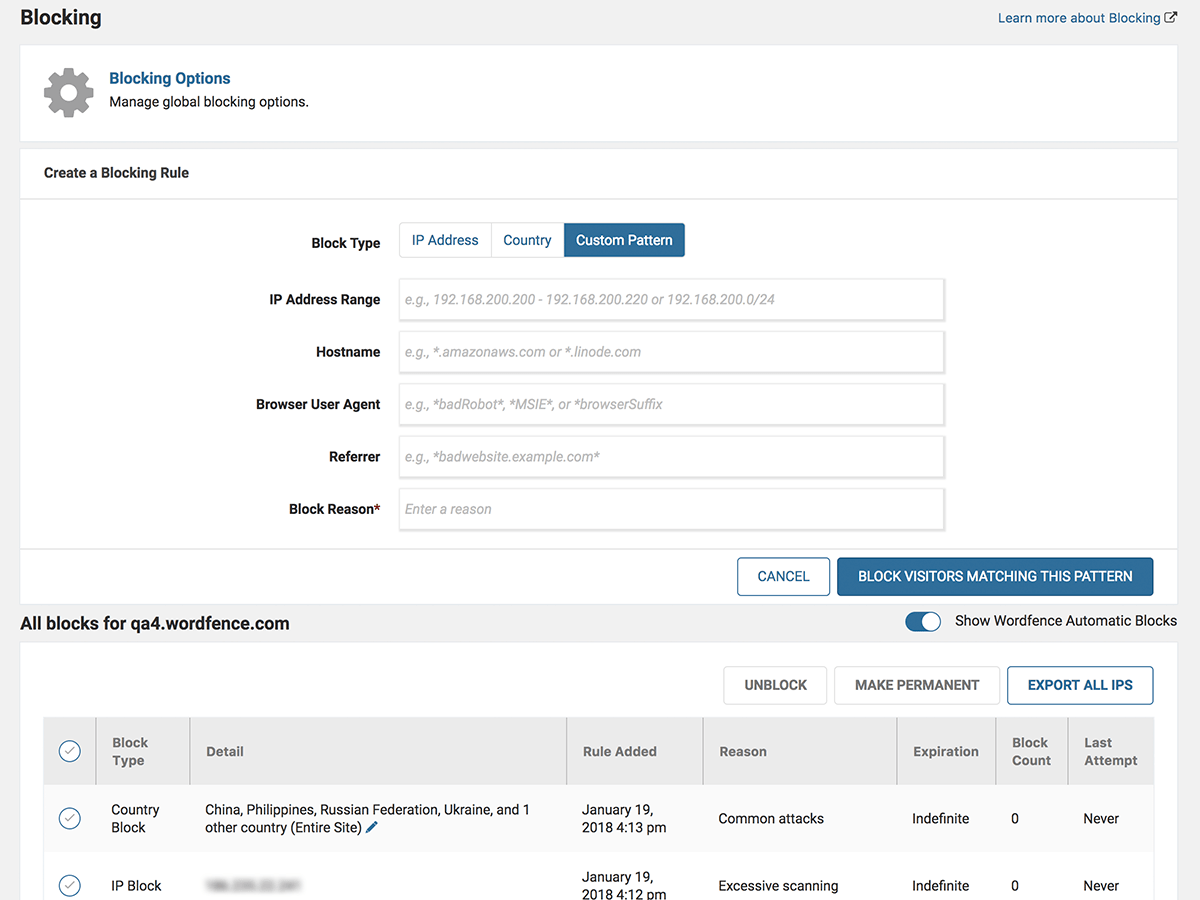
What Wordfence Security highlights on its WordPress.org page and its own website, split by version.
19 of 26 features we track in Security Plugins, feature score 80/100
Filters malicious requests (SQL injection, XSS and similar) before they reach WordPress.
Endpoint WAF in free version; free rules arrive 30 days after Premium.
Firewall runs on the vendor's network in front of your server, not inside WordPress.
Firewall runs on your server inside WordPress, not on a vendor network.
Limits failed logins and locks out attackers guessing passwords.
Limits login attempts and locks out attackers.
CAPTCHA or Turnstile on login, registration and password reset forms.
reCAPTCHA-based CAPTCHA on the login page in the free plugin.
Throttles or blocks aggressive crawlers and bad bots.
Can rate-limit or block aggressive crawlers, scrapers and bots.
Block or allow traffic by country.
Country blocking requires Wordfence Premium.
Blocks IPs known for attacks using shared threat intelligence.
Real-time IP blocklist from Wordfence threat intel is Premium-only.
Scans files and database for malware, backdoors and injected code.
Scans files for malware, backdoors, SEO spam and malicious URLs.
Compares core, plugin and theme files with originals and flags changes.
Compares core, theme and plugin files with WordPress.org copies and can repair them.
Warns when installed plugins, themes or core have known vulnerabilities.
Scan flags plugins and themes with known vulnerabilities or abandoned code.
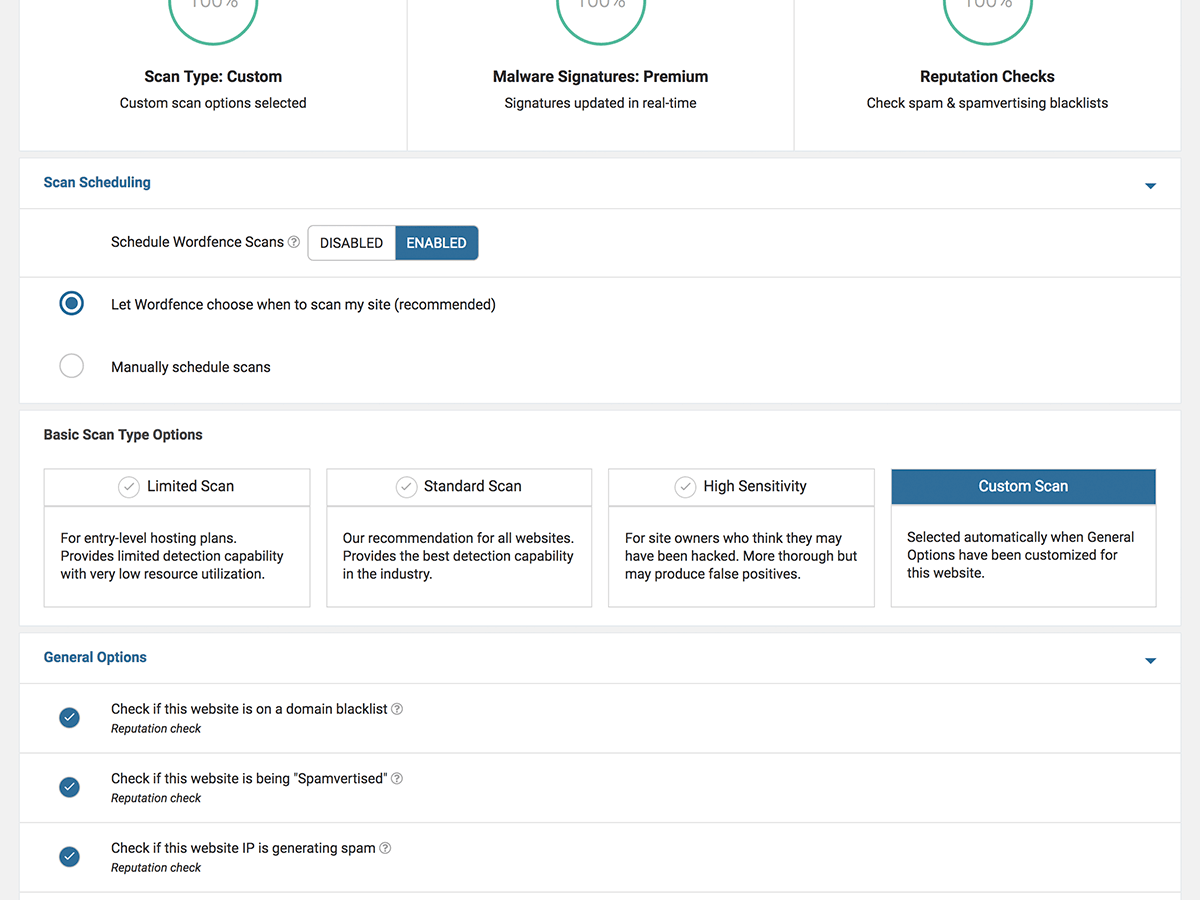
Runs scans automatically on a schedule.
Scans run on a schedule; Premium allows more frequent and custom scans.
Scans run on the vendor's servers so they don't slow your site.
Scans run on your own server and use its resources.
One-click or expert cleanup of infected sites.
Analyst-led malware cleanup included from the Care plan.
Second login factor via authenticator app, email or similar.
TOTP authenticator-app 2FA, including WooCommerce integration.
Passwordless login with passkeys or hardware security keys.
Passkey sign-in available in both free and premium versions.
Enforce strong passwords, expiry or breached-password checks.
Blocks administrator logins that use known compromised passwords.
Move or hide the wp-login.php / wp-admin login page.
No option to move or rename wp-login.php.
View and end active user sessions, limit concurrent logins.
No tool to view or end active user sessions.
Disable XML-RPC, file editing, user enumeration and similar weak points.
XML-RPC disabling and REST API user-enumeration protection; no broader hardening checklist.
Enforce HTTPS, fix mixed content and redirects.
No HTTPS enforcement or mixed-content tools.
Set HSTS, CSP, X-Frame-Options and other HTTP security headers.
Does not manage HTTP security headers.
Firewall rules that block exploits for known plugin vulnerabilities before an update is available.
Firewall rules block exploits for known vulnerabilities; free rules are delayed 30 days.
Automatically updates plugins with known vulnerabilities.
Warns about vulnerable plugins but does not auto-update them.
Records logins, changes and admin actions for auditing.
Audit Log of user, plugin, theme and content changes is Premium.
Email or app alerts for attacks, lockouts and scan results.
Email alerts in the plugin; Central adds SMS and Slack alerts.
Manage security for many sites from one dashboard.
Wordfence Central manages unlimited sites for free.
On WordPress.org
1 site
Real-time firewall rules, malware signatures and IP blocklist; country blocking; 30-day audit log history; priority ticket support.
1 site
Everything in Premium plus dedicated analyst, yearly security audit, malware removal and incident response; 6-month audit log.
1 site
Everything in Care plus 24/7/365 incident response with a 1-hour response time; 1-year audit log.
Prices are list prices from the vendor's site, checked 14 Oct 2026. Many vendors discount the first year.
Free installs from WordPress.org, the vendor's own claim, and our estimate of paid installs.
Active installations reported by WordPress.org.
The vendor does not publish a total.
Our estimate, see method below.
How we estimated this: About 7.5M free installs x 5.6% (the usual share of free sites that also run the paid version when some key features are paid, lower for very large free bases) gives 420K. Likely range: 210K to 840K. This counts sites running the paid version, including sites whose licence has lapsed. Estimates are rough and based on public figures as of 14 Oct 2026.
276,359 downloads last week, 432.1M all time
| Version | 9.0.2 |
|---|---|
| Last updated | 30 Sep 2026 (34 days ago) |
| Tested up to | WordPress 7.1.4 |
| Requires | WordPress 4.7+, PHP 7.0+ |
| Support threads (2 months) | 151 of 183 resolved |
| On WordPress.org since | 21 Apr 2012 |
 Limit Login Attempts Reloaded/Wordfence Security
 Kadence Security (formerly Solid Security)/Wordfence Security
 Patchstack/Wordfence Security
 Wordfence Security/WP Cerber Security
 MalCare Security/Wordfence Security
 Shield Security/Wordfence Security
 Defender Security/Wordfence SecuritySucuri Security/Wordfence Security
 All-In-One Security (AIOS)/Wordfence Security
 Really Simple Security/Wordfence Security
 Jetpack Protect/Wordfence Security
Free auditing, file integrity and remote scanning plugin from Sucuri that connects to its paid cloud firewall and malware cleanup platform.
WPMU DEV's WordPress security plugin with malware scanning, AntiBot firewall, 2FA with passkeys, hardening and audit logs; Pro adds scheduled scans.
Automated WordPress security plugin with firewall, silentCAPTCHA bot detection, 2FA and audit log; ShieldPRO adds malware and vulnerability scanning.
Cloud-scanning WordPress security plugin with a plugin-level firewall, login protection and paid one-click malware cleanup, for site owners and agencies.
Login-focused WordPress security plugin (formerly Solid Security / iThemes Security) with 2FA, brute-force protection and Patchstack virtual patching in Pro.
Self-distributed WordPress security plugin with firewall, anti-spam, malware scanner, 2FA and custom login URL; PRO adds GEO rules and scheduled scans.
Yes. Wordfence Security has a free version on WordPress.org. Paid plans start at $149/yr.
WordPress.org reports 5M+ active installations of the free version. We estimate around 420K sites run the paid version.
Yes: included. Endpoint WAF in free version; free rules arrive 30 days after Premium.
Yes: included. Limits login attempts and locks out attackers.
Yes: included. Scans files for malware, backdoors, SEO spam and malicious URLs.
Yes: included. Scan flags plugins and themes with known vulnerabilities or abandoned code.
Yes: included. TOTP authenticator-app 2FA, including WooCommerce integration.
Yes: paid version (Premium). Audit Log of user, plugin, theme and content changes is Premium.
For many sites it is a solid baseline: the firewall, scanner, 2FA and passkeys are all free. The main gap is that free sites receive new firewall rules and malware signatures 30 days after Premium customers.
The plugin can repair modified core, theme and plugin files itself. Hands-on malware removal by Wordfence analysts is included in the Care and Response plans.
No. It runs on your own server inside WordPress, so it does not provide a CDN or network-level DDoS mitigation, but it also does not need DNS changes.
Yes. Wordfence Central is free for unlimited sites and shows security status, scan findings and alerts for every connected site.
Last updated 5 Oct 2026. Spotted something wrong? Suggest an edit.